信息通信技术与政策

信息通信技术与政策

信息通信技术与政策 ›› 2026, Vol. 52 ›› Issue (8): 74-81.doi: 10.12267/j.issn.2096-5931.2026.08.011

专题:数字安全与应用 上一篇    下一篇

基于大模型驱动的新型智能体安全软件测试方案研究

A novel agent security software testing scheme driven by large language model

韩涵1, 王景尧2, 常天恩2   

  1. 1 北京中数睿智科技有限公司, 北京 100083
    2 中国信息通信研究院泰尔终端实验室, 北京 100191
  • 收稿日期:2026-06-20 出版日期:2026-08-25 发布日期:2026-09-02
  • 作者简介:
    韩涵,北京中数睿智科技有限公司董事长,长期从事人工智能应用和大模型新技术研究工作,主要研究方向为人工智能大模型、复杂决策等;
    王景尧,中国信息通信研究院泰尔终端实验室数字生态发展部主任,高级工程师,长期从事数字化技术的应用研究工作,主要研究方向为人工智能、数字化转型、数据安全等;
    常天恩,中国信息通信研究院泰尔终端实验室数字生态发展部助理工程师,主要研究方向为数字化转型和数字安全等

HAN Han1, WANG Jingyao2, CHANG Tianen2   

  1. 1 Zensmart Technology Co., Ltd., Beijing 100083, China
    2 CTTL Terminal Labs, China Academy of Information and Communications Technology, Beijing 100191, China
  • Received:2026-06-20 Online:2026-08-25 Published:2026-09-02

摘要:

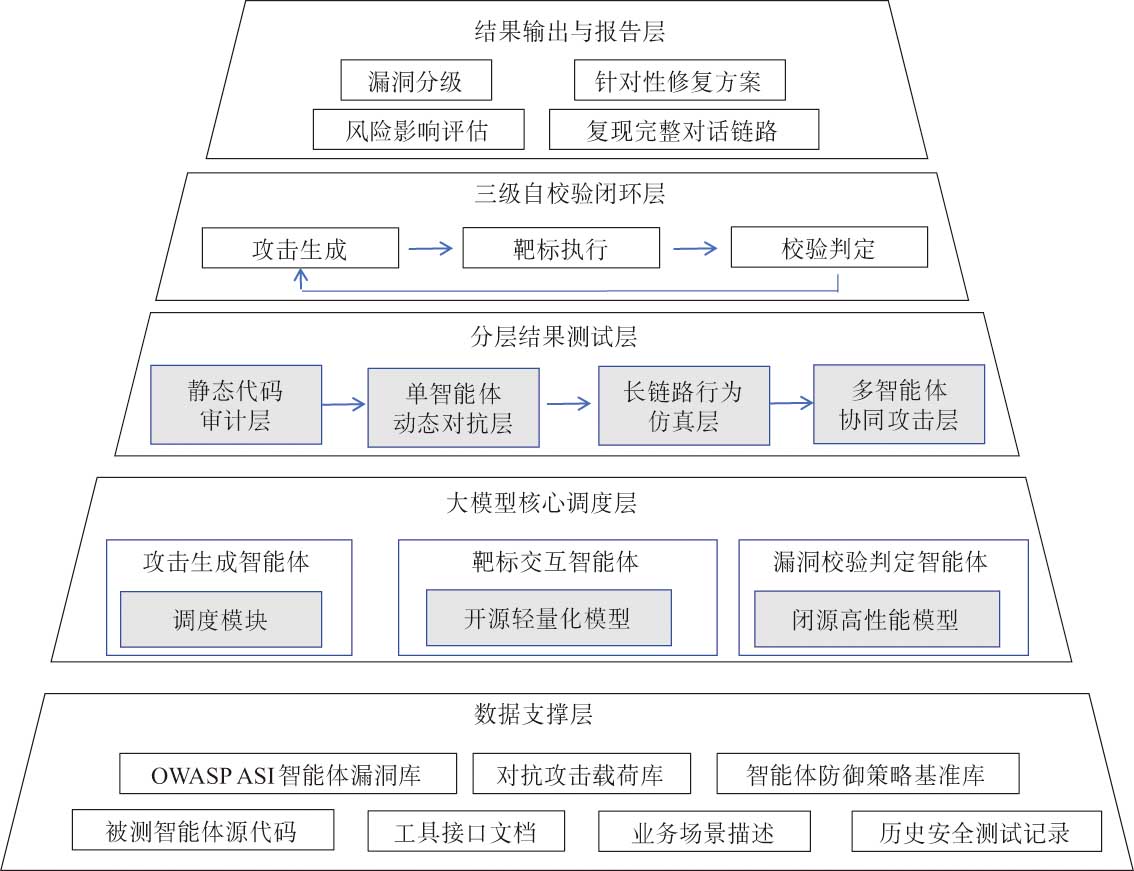
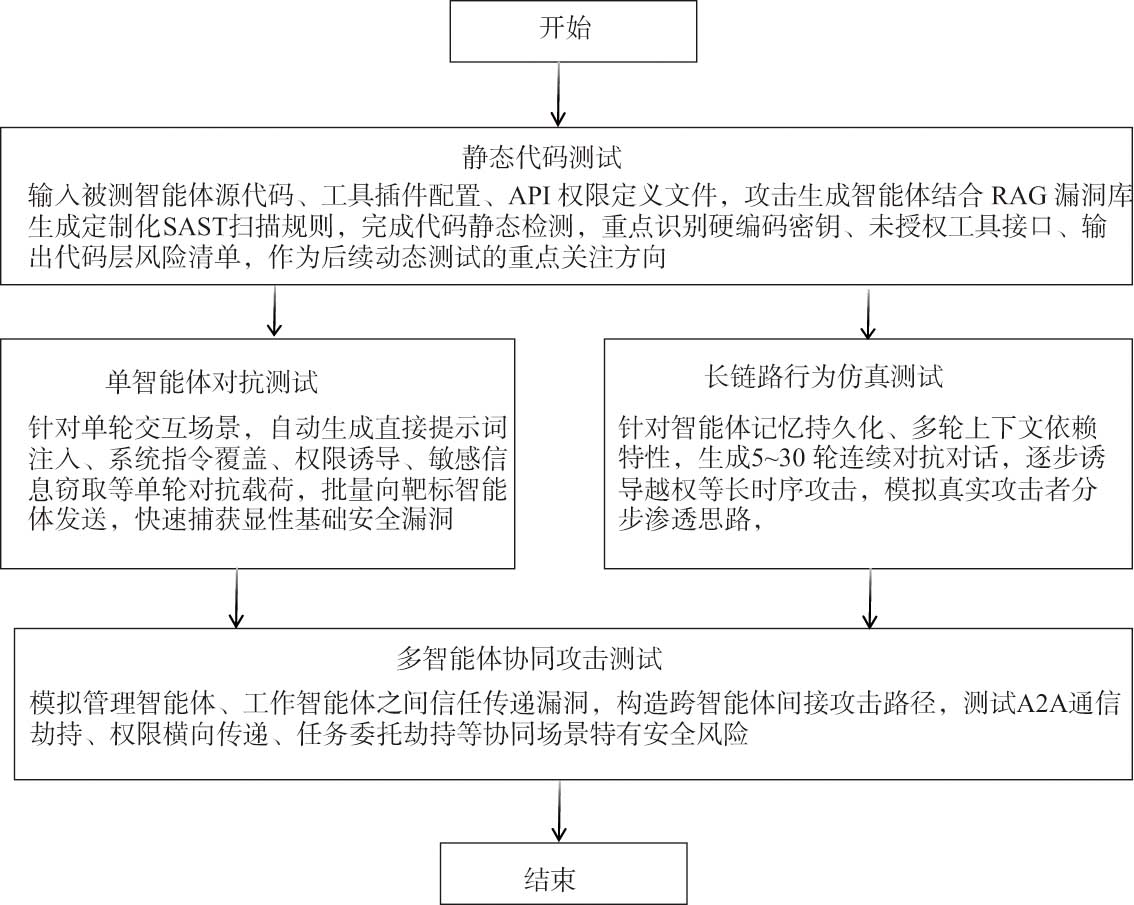
目前,智能体面临提示词注入、工具越权调用、上下文投毒、多智能体信任劫持等多种新型安全漏洞。传统静态代码扫描、动态 Payload 爆破、人工红队渗透等测试手段,存在漏洞检出准确率低、误报率高、无法覆盖长链路涌现风险、测试用例生成效率不高等短板。基于此,面向智能体全生命周期安全验证需求,提出一种检索增强大模型驱动的分层式智能体安全测试方案。该方案能够有效识别传统测试方案无法捕获的多步链式涌现安全缺陷,可为智能体软件安全标准化测试提供完整的技术路径。

关键词: 智能体, 安全测试, 大语言模型, 检索增强生成, 漏洞检测

Abstract:

With the large-scale deployment of autonomous AI Agents in low-altitude intelligent network, industrial control, financial services and urban governance, new security vulnerabilities such as prompt injection, unauthorized tool calling, context poisoning and multi-agent trust hijacking continue to break out. Traditional testing methods including static code scanning, dynamic payload blasting and manual red team penetration suffer from low vulnerability detection accuracy, high false positive rate, inability to cover emergent risks in long link tasks and insufficient efficiency of test case generation. A hierarchical agent security testing scheme driven by retrieval-augmented large language model is proposed to meet the full-lifecycle security verification requirements of AI Agents. The scheme can effectively identify emergent security defects in multi-step chains that cannot be captured by traditional testing solutions, providing a complete technical path for standardized security testing of agent software.

Key words: agent, security testing, large language model, retrieval-augmented generation, vulnerability detection

中图分类号: